A small business security plan begins with the work it cannot afford to lose. Identify essential systems, important information and the people who can restore operations. Then assign practical protections and review dates rather than relying on a list of purchased products.
List the essential services
Include email, business accounts, customer records, order processing, website administration and any specialised operational system. Record the owner, administrator, supplier and recovery contact. Check whether a former employee or contractor still has access.
Identify which information needs stronger protection and where it is copied. A forgotten shared file or unmanaged device can be important even when it is outside the main application.
Protect accounts and maintain software
Use unique credentials, appropriate password management and multifactor authentication for important accounts. CISA’s small business MFA guidance explains why an additional authentication factor matters. Record the approved recovery route so a lost device does not force an unsafe bypass.
Assign responsibility for software updates and unsupported systems. Test changes appropriately for essential applications, but do not let uncertainty turn into an indefinite lack of maintenance. Include supplier-managed systems in the ownership record.
Verify backups and restoration
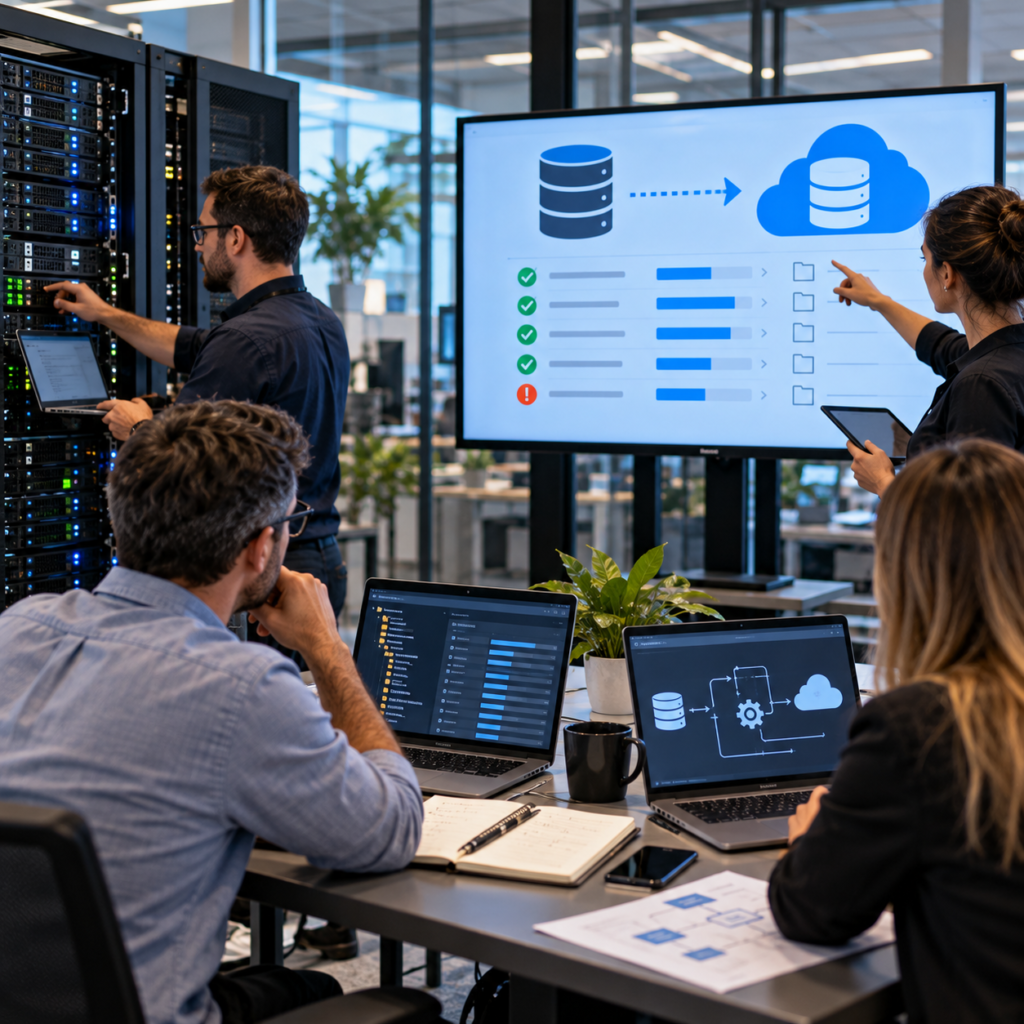
Record what is backed up, how often and who can access the recovery copy. Confirm that the backup covers the information and configuration needed to resume work. Cloud hosting or file synchronisation alone does not establish that your intended recovery is possible.
Restore an approved sample in a safe environment and verify the result. Include the time and skills required. A successful backup notification is useful evidence of a job completing, but it is not a complete restoration test.
Make reporting easy
Tell staff how to report a suspicious message, lost device or unexpected account activity. Use a known contact route and avoid blame that discourages early reporting. Do not ask people to investigate suspicious files themselves.
Prepare contacts and responsibilities for an incident. The team needs to know who can coordinate with suppliers, decide which operations pause and obtain advice on any applicable reporting obligations.
Maintain a practical review cycle
Record gaps, owners and next actions. Include access changes after staff departures and changes to suppliers or important applications. Use the security evidence and recovery worksheet to check that the planned controls work. Specialist support can follow the technology support decision guide.