A business data migration is not simply a transfer from one system to another. It changes where employees find information, how applications exchange records, which reports leaders trust, and whether daily transactions can continue without interruption. A technically successful transfer can still become an operational failure if customer histories are incomplete, identifiers no longer match, integrations break, or users cannot perform essential tasks.
The migration steps described by Small Business Trends provide a useful starting point: plan the project, inspect and back up the data, design the migration, execute it, and validate the result. Operators should turn those steps into explicit approval gates. Before authorizing a cutover, leadership needs evidence that the scope is controlled, ownership is clear, data defects are understood, dependencies have been tested, and recovery is possible.
Define the business outcome before defining the transfer
Begin with the operational reason for moving the data. Replacing an accounting platform, consolidating customer records after an acquisition, and moving inventory data into a new enterprise system create different risks. The project charter should identify the business processes affected, the capabilities required on day one, and what can be deferred.
Translate the objective into a migration scope that names:
- source and target systems;
- data domains, tables, files, and historical periods included;
- records that will be archived rather than migrated;
- integrations, reports, workflows, and user roles affected;
- legal, contractual, retention, privacy, and audit requirements;
- the business operations that cannot tolerate interruption.
Do not let “move all the data” substitute for a scope decision. Historical information may need to remain searchable without being loaded into the live target system. Conversely, excluding old records can be risky when they support warranties, customer service, tax documentation, or regulatory obligations.
Define measurable acceptance criteria before mapping begins. These may include successful reconciliation of record counts and control totals, correct handling of required fields, functioning integrations, preservation of access restrictions, and completion of critical workflows by representative users. The specific thresholds should reflect business consequences rather than technical convenience.
Assign accountable owners and expose dependencies
A migration needs one accountable business sponsor, but no single person can validate every data domain. Establish ownership at three levels. The sponsor approves scope, downtime, residual risk, and cutover. A migration lead coordinates mapping, extraction, transformation, loading, testing, and issue management. Data owners from functions such as finance, sales, operations, and compliance decide what records mean and approve their migrated domains.
Technical teams should own execution, security controls, environments, interfaces, monitoring, and recovery procedures. Process owners should test whether work can actually be completed. Someone who understands order fulfilment, for example, is better placed than a developer to notice that migrated orders have lost delivery instructions or tax treatment.
Next, create a dependency map. Trace how data enters the source, where it is transformed, which applications consume it, and what outputs depend on it. Include scheduled imports, APIs, spreadsheet exports, identity services, payment or fulfilment connections, dashboards, regulatory reports, and automated notifications. Undocumented manual workarounds deserve particular attention because they may disappear when the source system is retired.
For every dependency, record an owner, test method, cutover action, and fallback. This converts a vague integration inventory into an operational control plan.
Profile data before deciding how to transform it
The source recommends auditing and cleaning data before migration. For operators, the important distinction is between defects that can be corrected systematically and ambiguities that require a business decision.
Profile each in-scope domain for missing required values, duplicates, invalid formats, orphaned records, inconsistent labels, obsolete entries, incompatible identifiers, and unexpected volumes. Compare the source structure with the target model. A single source field may need to be split, several values may need to be standardized, or a target field may have no reliable source equivalent.
Create a transformation rule for every mismatch and assign its approval to the relevant data owner. Do not silently invent values to satisfy a target system. If a mandatory field cannot be populated reliably, agree whether to correct the source, derive the value under a documented rule, place the record in an exception queue, or exclude it with formal approval.
Preserve an untouched, access-controlled backup before extraction and confirm that it can be restored. Also maintain traceability between source records, transformation rules, exceptions, and target results. That audit trail is essential when users challenge a balance, status, address, or transaction after launch.
Test the migration as a business process
A rehearsal should use the same extraction, transformation, loading, security, and reconciliation procedures planned for production. Test with representative data, including duplicates, blank fields, special characters, unusual dates, large records, inactive accounts, and records linked across multiple tables.
Use several layers of validation:
- Structural testing: confirm schemas, formats, relationships, and required fields.
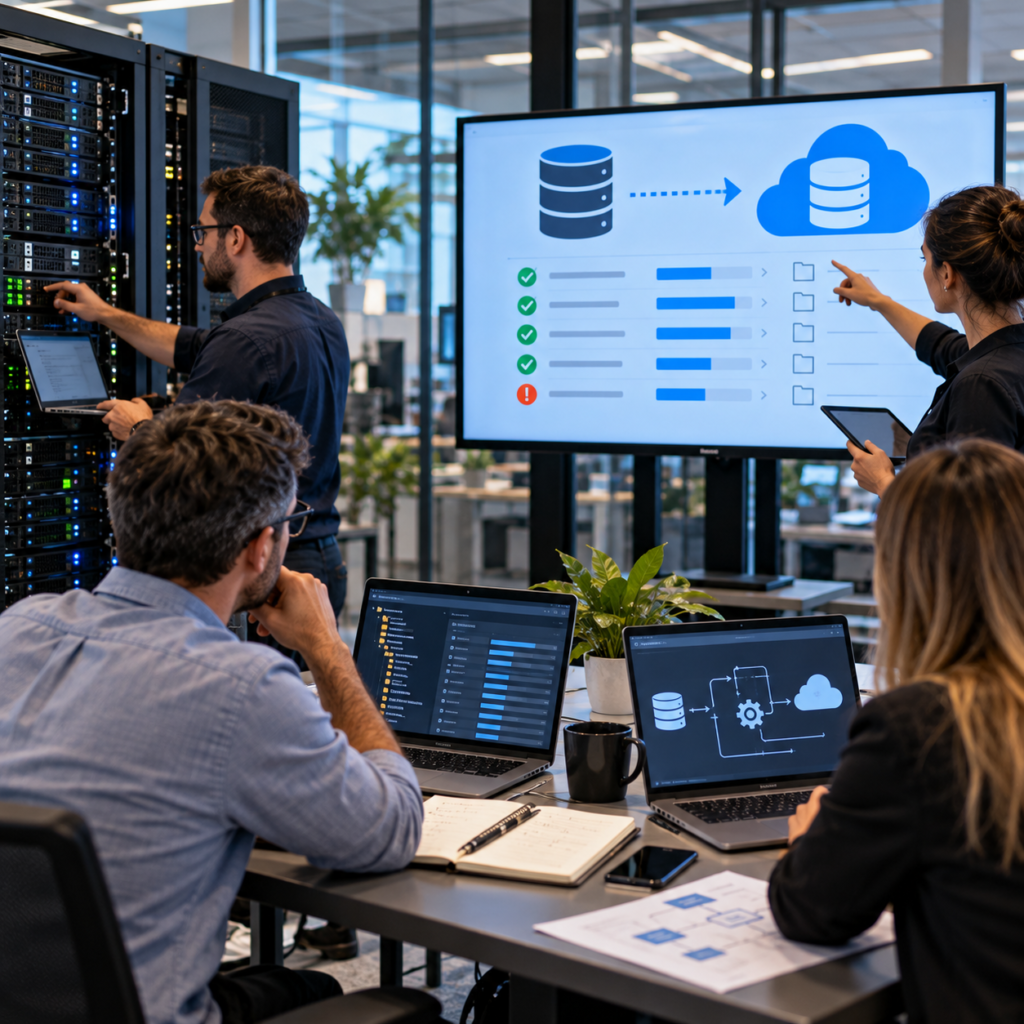
- Reconciliation: compare record counts, financial or quantity control totals, and sampled source-to-target values.
- Functional testing: complete critical tasks such as creating an order, issuing an invoice, finding a customer history, or producing a required report.
- Integration testing: verify upstream and downstream data flows, including failures and retries.
- Access testing: ensure users can reach only the records and functions appropriate to their roles.
- Operational testing: measure whether the migration and validation can finish inside the available cutover window.
Log every defect with severity, owner, due date, retest status, and cutover impact. A passed test should include evidence, not just a verbal confirmation. Business data owners should sign off their domains, while process owners approve end-to-end workflows.
Engineer cutover and rollback as controlled decisions
Choose between a single cutover, a phased migration, or a period of parallel operation based on dependencies and tolerance for disruption. A single event can simplify synchronization but concentrates risk. Phasing limits exposure but may require temporary interfaces and careful management of records split between systems. Parallel operation adds validation opportunities while creating extra work and the danger of conflicting updates.
The cutover runbook should specify the sequence, timing, owners, communication channels, source-system freeze, final extraction, validation steps, user access changes, integration activation, and go/no-go authority. Include decision points with deadlines. If validation is incomplete at the agreed checkpoint, the team should not improvise under pressure.
A rollback plan must say more than “restore the backup.” Define what triggers reversal, who can order it, how writes to the target will be handled, how the source will be restored or reopened, how integrations will be redirected, and how transactions created during the cutover window will be reconciled. Rehearse the procedure and estimate its duration through testing rather than assumption.
After launch, use a stabilization period with enhanced monitoring, a visible issue queue, rapid escalation, and daily reconciliation of critical data. Keep the legacy environment and migration evidence available for the approved retention period; do not retire them merely because the target system opens successfully.
Readiness checklist and reasons to delay
Approve cutover only when the team can answer yes to the following:
- The scope, exclusions, acceptance criteria, and critical processes are documented.
- Each data domain, dependency, test, and cutover task has a named owner.
- Data profiling is complete, and unresolved exceptions have explicit treatment.
- Transformation rules are documented and approved by business data owners.
- A protected source backup exists and restoration has been verified.
- Rehearsals have completed within the cutover window.
- Control totals, samples, workflows, integrations, and access controls have passed.
- Users, support teams, and affected partners understand the cutover plan.
- Go/no-go thresholds, rollback triggers, and decision authority are unambiguous.
- Post-launch monitoring and reconciliation have assigned owners.
Delay cutover when critical defects remain unexplained, reconciliation does not balance, required business owners have not approved results, the final rehearsal overruns the available window, dependencies remain untested, or rollback cannot be executed confidently. Also stop when source data continues changing without a synchronization plan or when teams cannot identify the authoritative system during transition.
The safest migration is not the one with no defects; it is the one in which defects, decisions, and recovery paths are visible before operations depend on the new system. Treat cutover approval as a business-risk decision supported by technical evidence, not as the inevitable final date on a project schedule.